CyberArmor
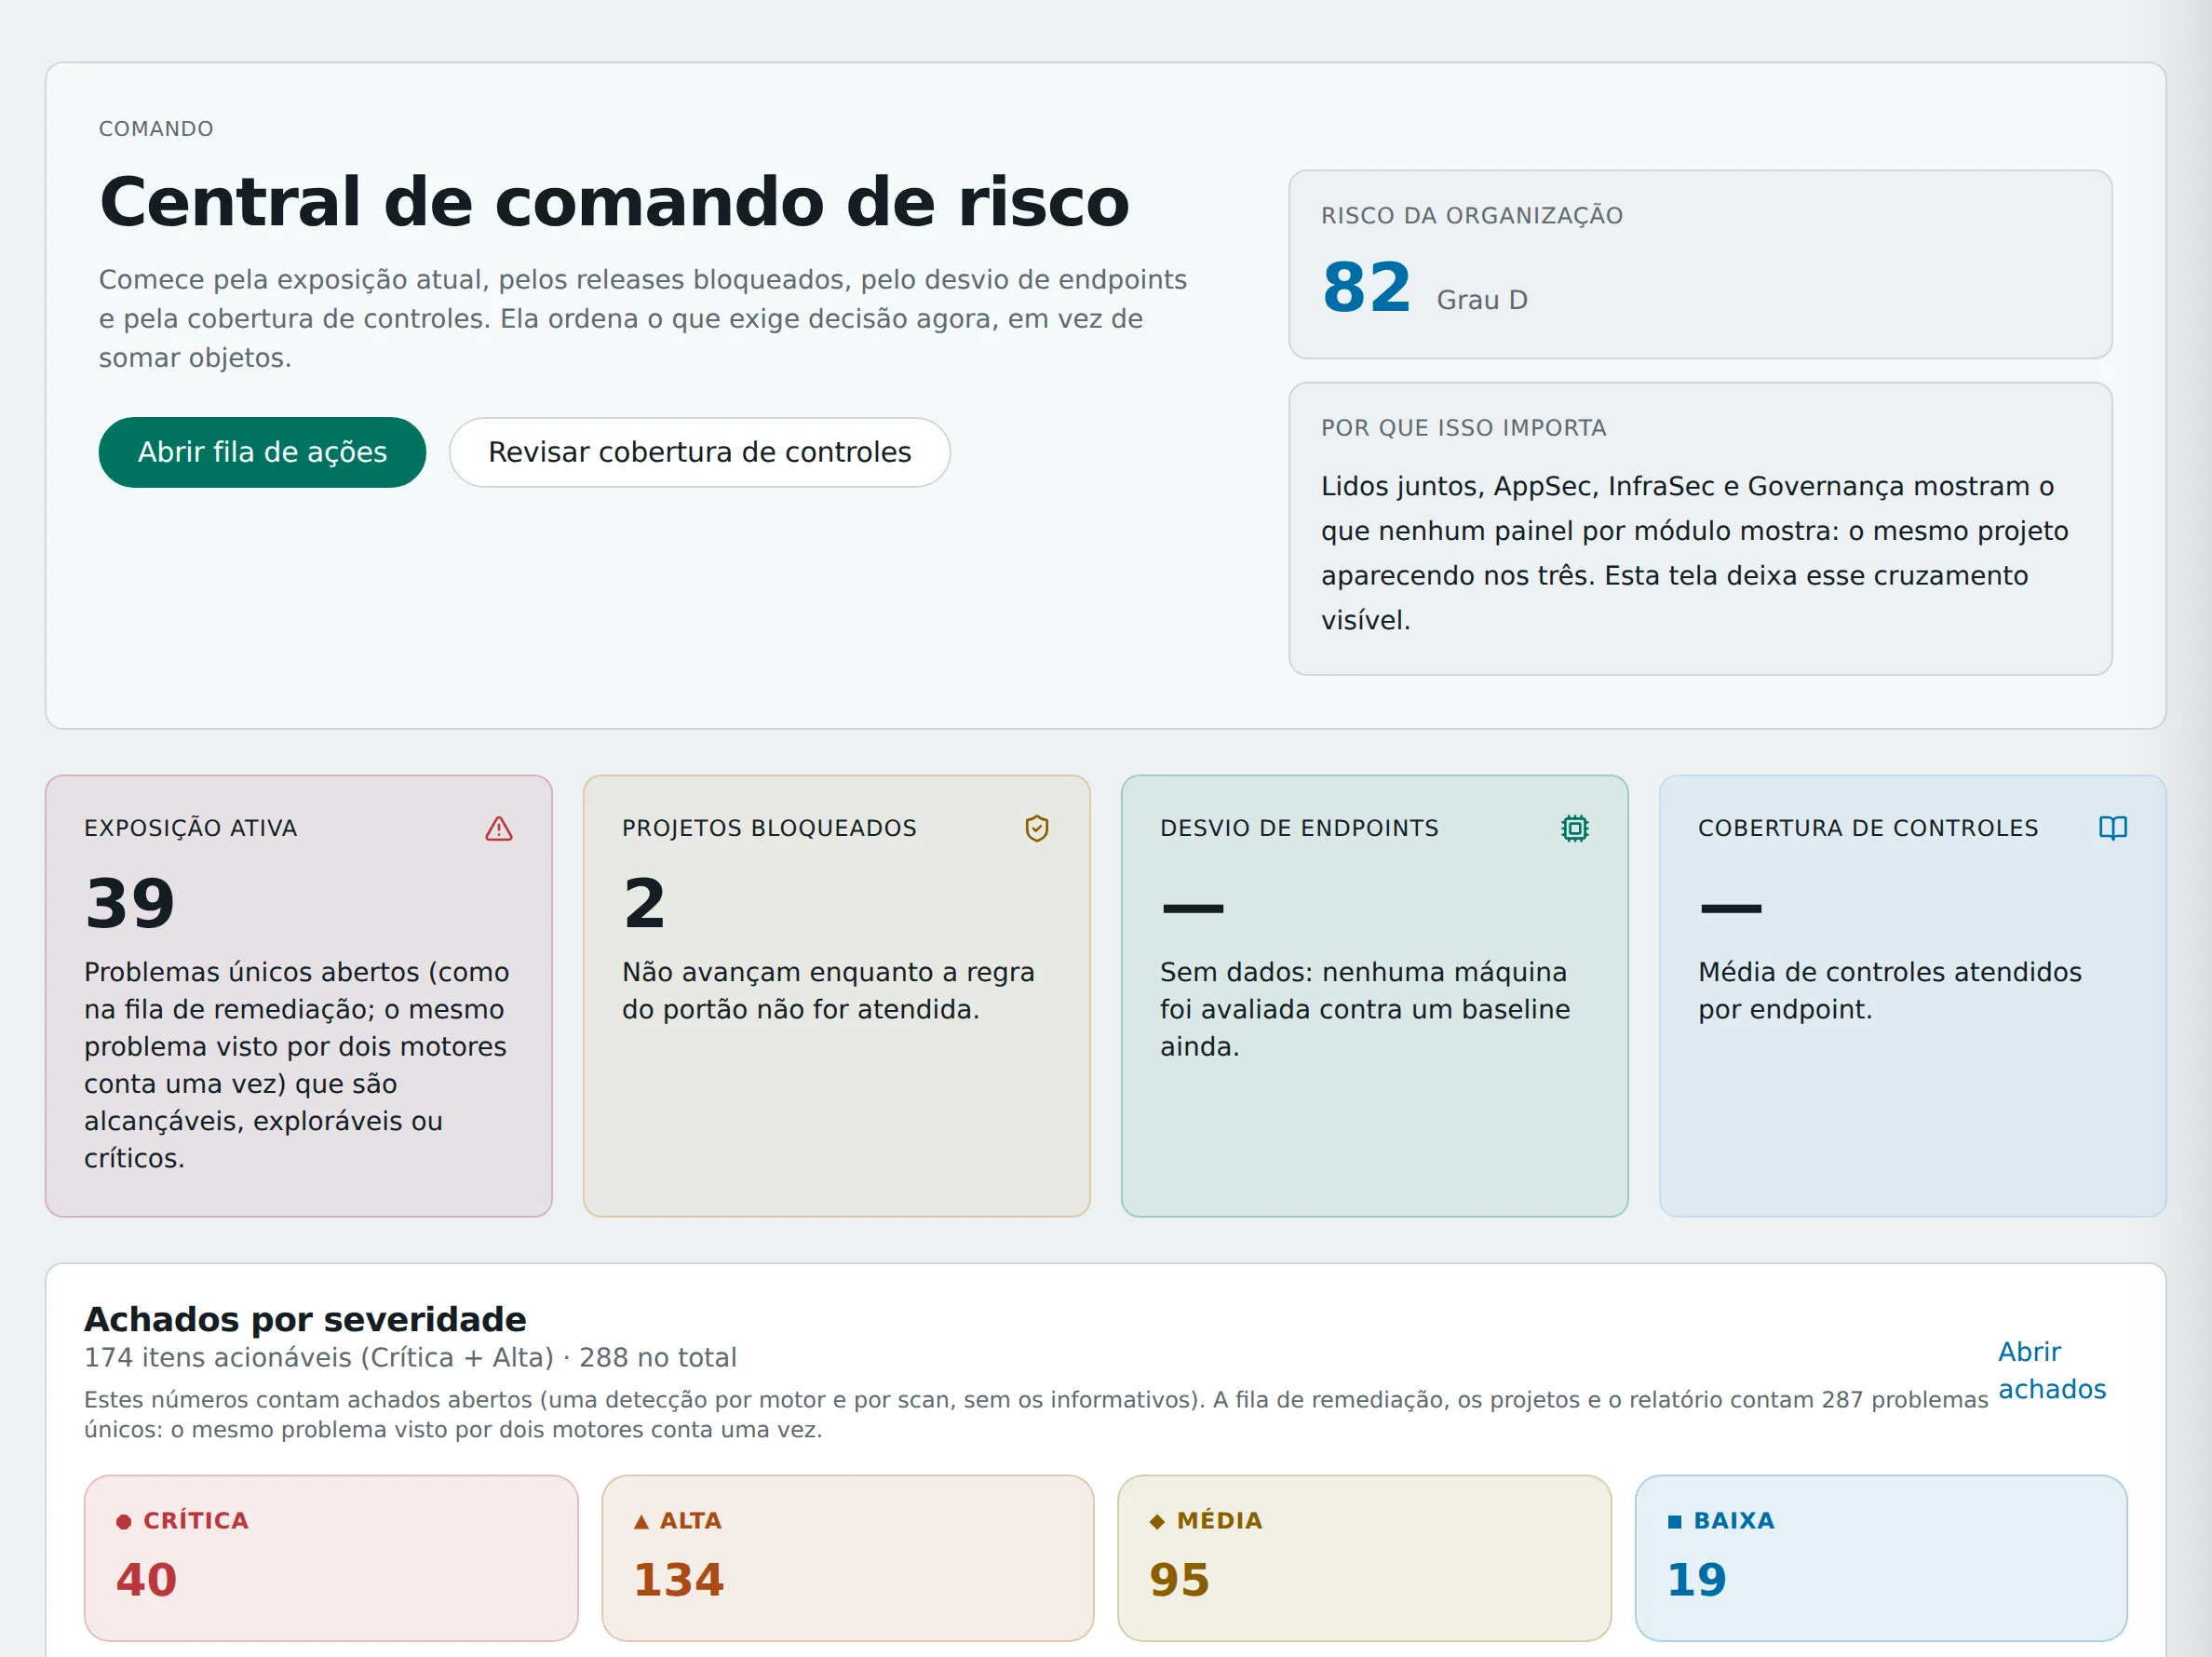
Imports what your security tools find, merges repeated results into a single finding and drafts the executive report.
See CyberArmorProvisional translation, under review.
Hegeon runs the assessment with your team and delivers the work on the CyberArmor platform. Every deliverable is recorded, with dates.
Software built in-house and used by our consulting team every day.
Imports what your security tools find, merges repeated results into a single finding and drafts the executive report.
See CyberArmorEach project takes 2 to 4 weeks and has a fixed price. At the end, you receive the report.
Shows which AI tools the company uses and what personal or confidential data shows up in them.
Fixed price quoted within 1 business day
Shows the software flaws an attacker can reach, in priority order.
Fixed price quoted within 1 business day
Compares the configuration of servers and workstations with public secure configuration benchmarks.
Fixed price quoted within 1 business day
Pick the problem your company has today.
A client asked for proof that your software is secure. Your development team has no security specialist.
Every server was set up a different way. The auditor wants proof of configuration.
LGPD or ISO 27001 now has a deadline. The evidence is scattered.
Employees use AI at work. The board does not know what data goes into it.
Five steps. In each one, you receive a concrete deliverable.
We learn your environment, the policies your company already has and what the auditor or your client is asking for.
You receive: a picture of the starting point, with the most urgent risks.
We order the work by business risk and by the deadline you need to meet.
You receive: the plan with priorities, owners and dates.
An assigned analyst carries out the plan within the rules of your environment. Every action is recorded.
You receive: the fixes applied and the record of each one.
After delivery, we keep watching configuration, vulnerabilities and controls. Your environment changes every week.
You receive: drift alerts and up-to-date evidence on the platform.
Each cycle ends with a report written for the board.
You receive: the report and dated evidence, ready for the audit.
Security bulletin, guides in Portuguese and a free AI use self-assessment with no sign-up.
Tell us what your company needs. You leave the call with three priorities for your environment.
Prefer to write? Use the email contato@hegeon.com.br.