Servers and workstations configured to your company’s policy, with proof for the audit.
A misconfigured machine is the most common way into an attack. Our analysts apply hardening, track configuration and vulnerabilities and show, machine by machine, what is compliant.
What infrastructure security is
A badly configured machine leaves doors open for an attacker, even with antivirus. Hardening means adjusting servers and workstations to close those doors, following public secure configuration benchmarks. Hegeon assesses your machines in 2 weeks, applies the rules according to your company policy and keeps the evidence for the audit.
These guides are published by independent organizations and by the system vendors themselves, and each rule says what to configure and how to check it.
Infrastructure services
The assessment is the starting point. It ends with a proposal for an ongoing service, if that makes sense.
- 2 weeksGood place to start
Machine assessment
Our analysts read the configuration and inventory of the machines in scope. You receive the list of the most exposed machines and what to fix first.
Fixed price quoted within 1 business day
- Ongoing
Ongoing hardening and compliance
Hardening means adjusting each machine’s configuration to close the gaps an attacker would use. The analyst applies the baseline and tracks drift every month.
- On request
Monitoring and response under contract, during the agreed hours and SLA
A dedicated team watches the alerts from your environment during the hours and under the SLA set in the contract and acts when something happens. Setup takes 30 to 60 days, and the timeline is set in the proposal.
What you receive
Every check is recorded on the platform, with a date.
- Hardening based on public secure configuration benchmarks and your company’s internal policy.
- Continuous monitoring of configuration and vulnerabilities.
- Software inventory per machine.
- A compliance report per machine.
- Remediation followed by the analyst, from finding to fix.
Systems covered
Windows, Linux and macOS, through the platform agent installed on each monitored machine.
How the work happens
Assessment
We install the agent on the machines in scope and read each one’s configuration and inventory.
You receive: a picture of your fleet and the most exposed machines.
Prioritized plan
We build the baseline from public secure configuration benchmarks and your company policy, and order the machines by risk.
You receive: the baseline you approved and the rollout plan.
Execution by our analysts
The analyst audits each rule before applying it and follows the change window your company sets.
You receive: the adjusted machines and a record of each change.
Continuous monitoring
The platform compares each machine with the baseline and warns when a setting drifts.
You receive: drift alerts and new vulnerability alerts.
Executive report
Each cycle closes with the per-machine compliance report and a summary for the board.
You receive: the report and dated evidence.
Who does the work
Experienced, certified analysts run each project. Every project has an assigned analyst who answers for the work from assessment to report.
- One assigned analyst per project, who is your direct contact.
- Every rule audited before it is applied, within your company’s change window.
- Every check and every change recorded on the platform, with a date.
The résumés and certifications of the assigned team are presented in the proposal.
Why Hegeon
What you get in every contract, from day one.
- An assigned analyst. Each project has an analyst who answers for the work from start to finish.
- Dated evidence. Every finding, fix and piece of evidence is recorded on our platform, with the date it happened.
- A deliverable at every step. You know what you receive in each of the five steps of the method.
- A report for the board. The executive report explains risk in business terms.
On the platform
Hardening baselines bring together secure configuration controls for Windows, Linux and macOS. Each one can be audited before it is applied.
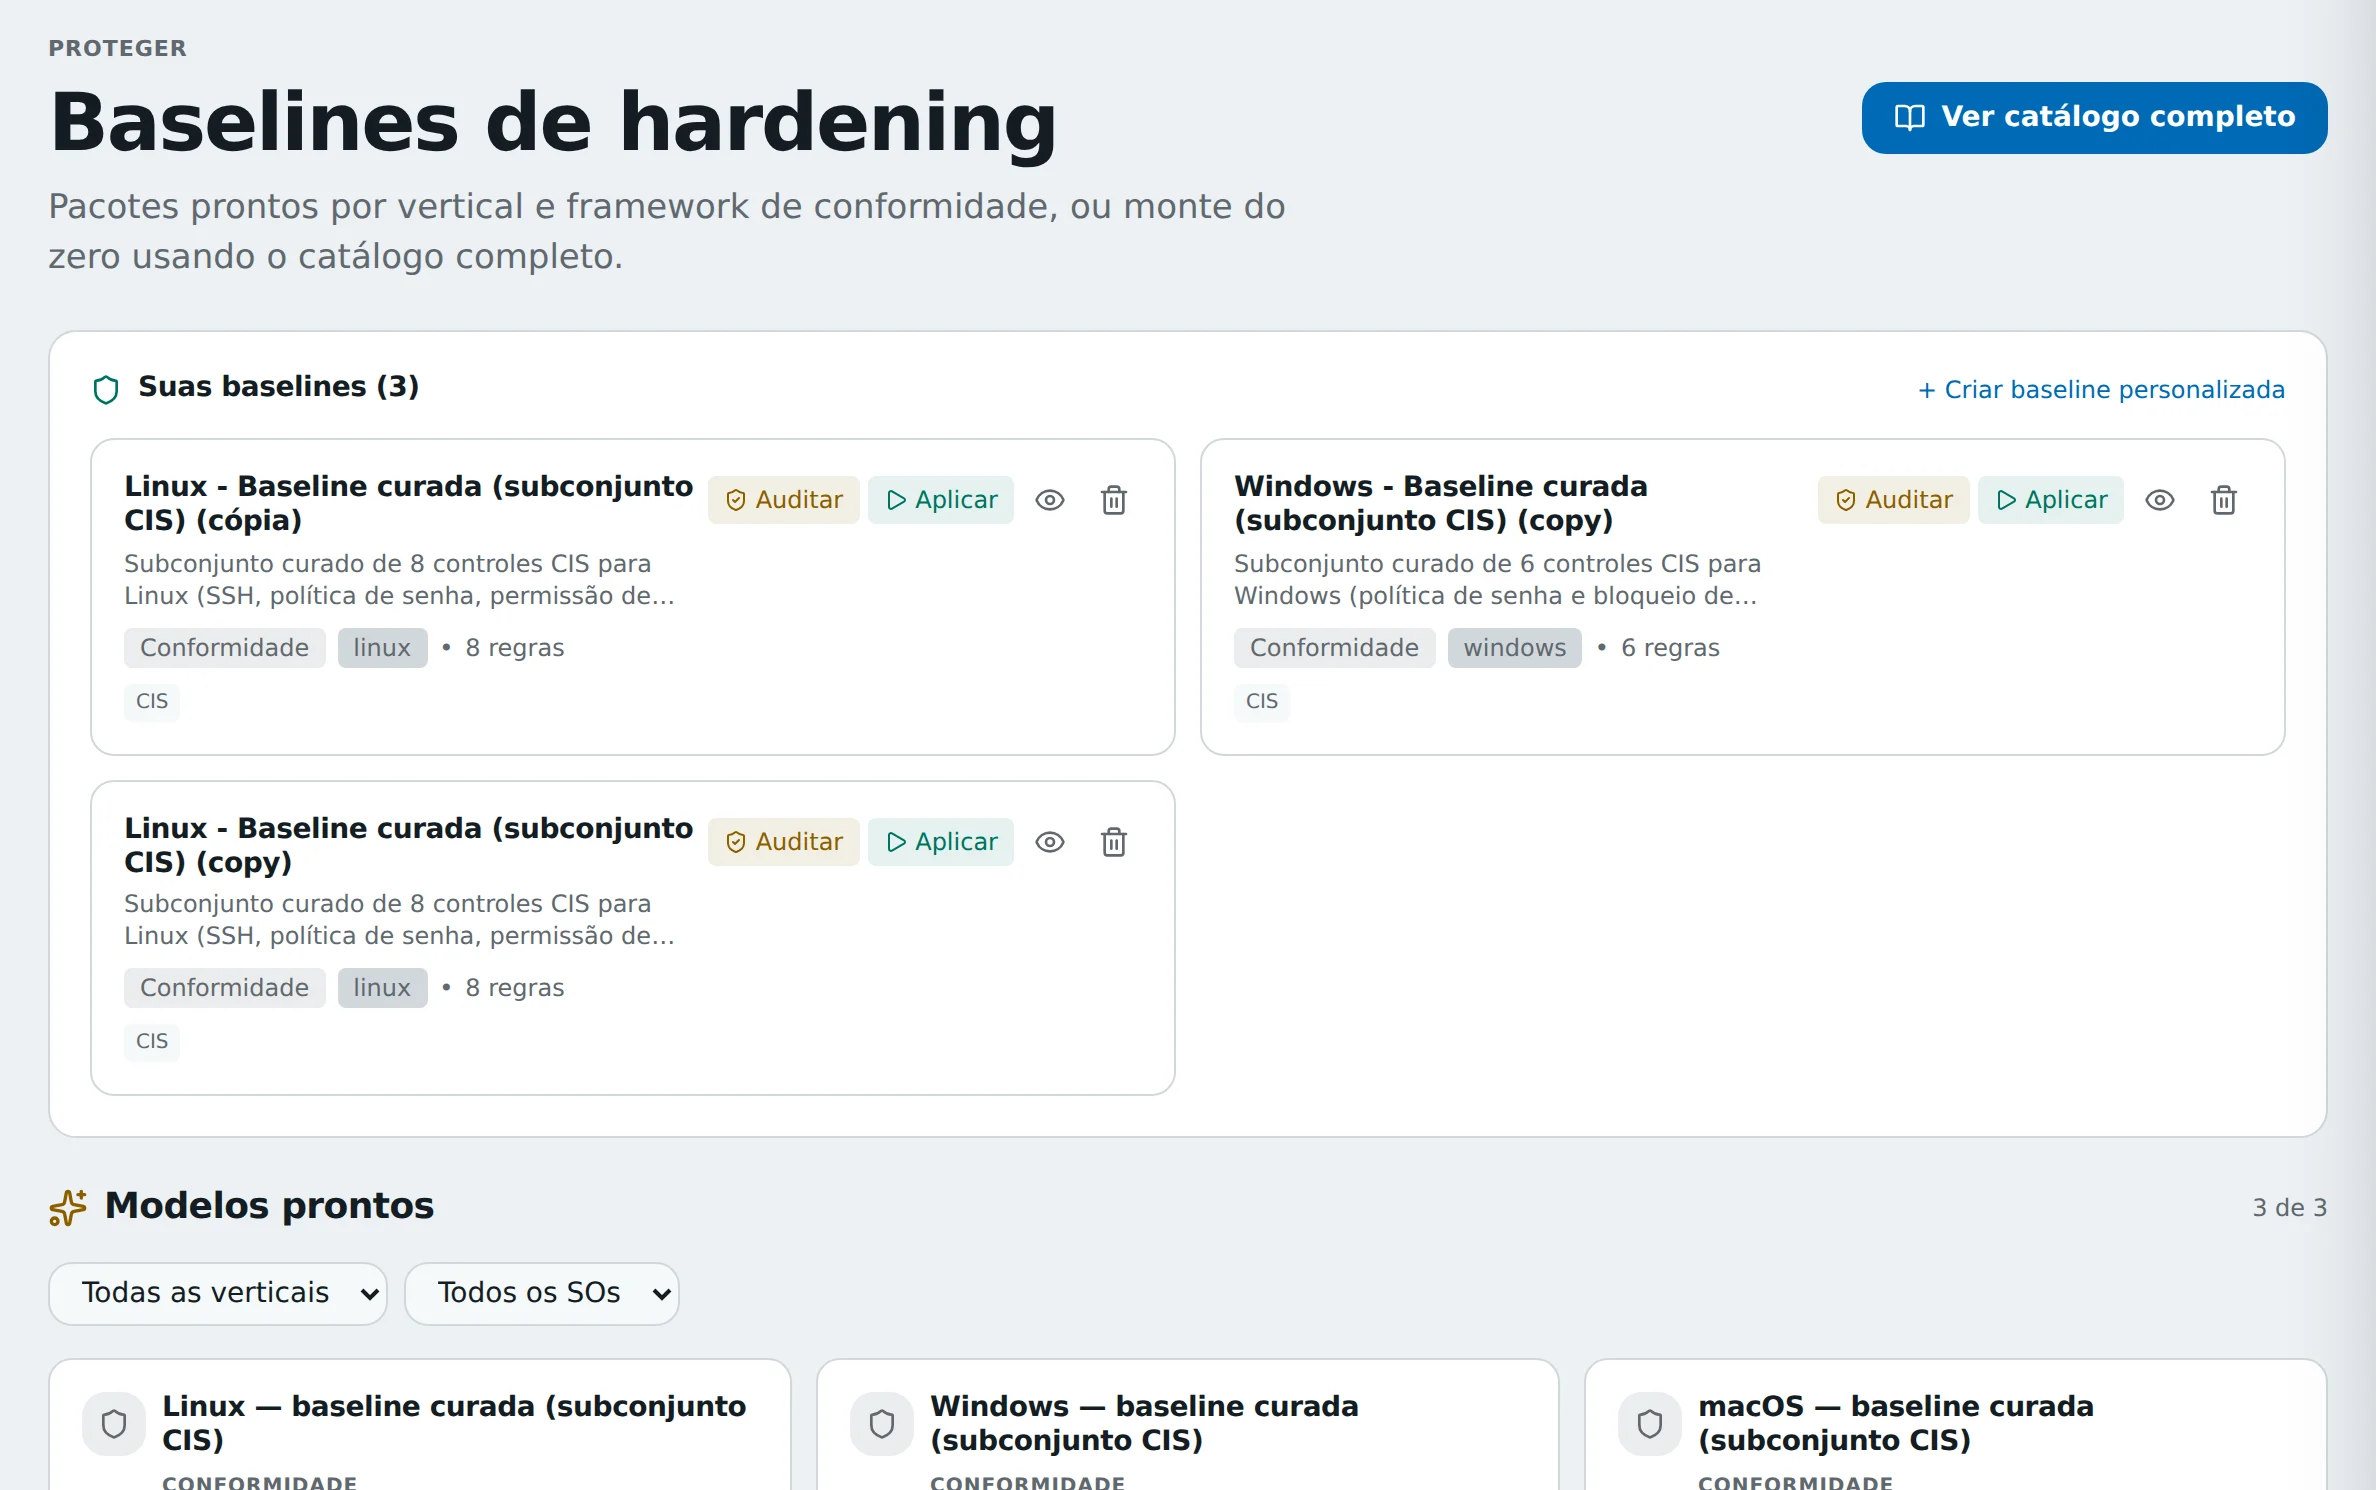
- Hardening baselines built from public secure configuration benchmarks.
- For each system, the audit and apply actions.
How to hire us
Every contract starts with a fixed project. It ends with a proposal for an ongoing service, if that makes sense for you.
- Fixed project
- Scope, timeline and price agreed before we start. It takes 2 to 4 weeks and ends with the report and the plan.
- Ongoing service
- An assigned analyst looks after your environment every month, with a monthly report and evidence on the platform.
Frequently asked questions
Do you do blue team work?
The blue team is the group that defends the environment: it configures, monitors and responds to incidents. In this practice, Hegeon handles the preventive part, with the machine assessment and the hardening of servers and workstations. Monitoring and response is available on request, during the agreed hours and SLA, with a dedicated team and an implementation timeline set in the proposal.
Do we need to install anything on the machines?
Yes. Each monitored machine gets the platform agent, which sends configuration and software inventory.
Do you apply a full public benchmark?
The platform’s ready-made templates use a subset of controls from public secure configuration benchmarks for Windows, Linux and macOS. The analyst adapts the baseline to your company policy.
Can hardening bring a system down?
That is why each rule is audited before it is applied. Rollout follows the change window agreed with your team.
How soon does monitoring start?
Setup takes 30 to 60 days, with a dedicated team. The exact timeline for your case is set in the proposal.
What is server hardening?
It means configuring the server to expose only what is needed: turning off unused services, tightening password and access rules and keeping updates current. The reference is public secure configuration benchmarks. At Hegeon, every rule is audited before it is applied, within the change window agreed with your team.
How long does the machine assessment take?
Two weeks. During that time, the platform agent collects the configuration and software inventory of each machine, and the analyst compares the result with public secure configuration benchmarks and your company policy. You receive a compliance report per machine and the order in which to fix things.
Talk to a specialist for 30 minutes.
Tell us what your company needs. You leave the call with three priorities for your environment.
Prefer to write? Use the email contato@hegeon.com.br.