Governance and compliance, with the evidence ready when the auditor asks.
A client, an auditor or the law will ask for proof that your company protects data. Our analysts organize policies, risks and evidence, and you follow everything on the platform.
What governance and compliance is
Without organized proof, a company loses time in the audit and is exposed to the ANPD, Brazil's data protection authority. Governance and compliance means keeping policies, risks, controls and evidence in order for the LGPD and ISO/IEC 27001. Hegeon leads LGPD compliance work, prepares the company for ISO 27001 certification and keeps every piece of evidence dated.
The LGPD is Brazil's personal data protection law. ISO/IEC 27001 is the international standard for information security management. The industry acronym for this work is GRC: governance, risk and compliance.
Governance and compliance services
GRC stands for governance, risk and compliance. Every service leaves its evidence recorded on the platform.
- Scoped per project
LGPD compliance
LGPD is Brazil’s General Data Protection Law. Our analysts map the personal data your company handles, point out the gaps and run the compliance plan.
- Scoped per project
ISO/IEC 27001 readiness
ISO/IEC 27001 is the international standard for information security management. We prepare your company for the certification audit, control by control.
- Ongoing
On-demand security officer (vCISO)
A vCISO is an information security officer who serves your company under contract. They run the security program and report to the board.
- First campaign within 30 days
Awareness with phishing simulation
Phishing is a fake message that tries to trick an employee into giving away a password or data. Our analysts send controlled simulations, measure who clicked and train the teams.
What you receive
Evidence is linked to each control, with the date it was produced.
- A gap analysis between what your company does today and what the standard or the law requires.
- Risk management, with owners and deadlines.
- Internal policies written for your reality.
- Mapping of the standard’s controls to your company’s practices.
- Collection and organization of evidence.
- Phishing campaign results, by department.
- An executive report for the board.
Standards already on the platform
ISO/IEC 27001:2022, NIST CSF 2.0, SOC 2 and OWASP SAMM, each with its controls. LGPD is covered in the compliance work.
We prepare your company for the audit. Certification is issued by an accredited certification body.
How the work happens
Assessment
We compare your company’s practices with the chosen standard or law, control by control.
You receive: the gap analysis and the most urgent risks.
Prioritized plan
We order the controls by risk and by the audit date.
You receive: the compliance plan with owners and deadlines.
Execution by our analysts
The analyst writes the policies with your team, assesses each control and gathers the evidence.
You receive: approved policies and assessed controls on the platform.
Continuous monitoring
The platform warns when a piece of evidence expires or a control needs a new assessment.
You receive: a compliance index that stays up to date.
Executive report
Before the audit, we review everything with you and close the report for the board.
You receive: the report and the evidence package for the auditor.
Who does the work
Experienced, certified analysts run each project. Every project has an assigned analyst who answers for the work from assessment to report.
- One assigned analyst per project, who is your direct contact.
- The same method across all four practices, from assessment to executive report.
- Every policy, control and piece of evidence recorded on the platform, with a date.
The résumés and certifications of the assigned team are presented in the proposal.
Why Hegeon
What you get in every contract, from day one.
- An assigned analyst. Each project has an analyst who answers for the work from start to finish.
- Dated evidence. Every finding, fix and piece of evidence is recorded on our platform, with the date it happened.
- A deliverable at every step. You know what you receive in each of the five steps of the method.
- A report for the board. The executive report explains risk in business terms.
On the platform
Each ISO/IEC 27001 control appears with its compliance status and a button to attach evidence. The index shows how much is left.
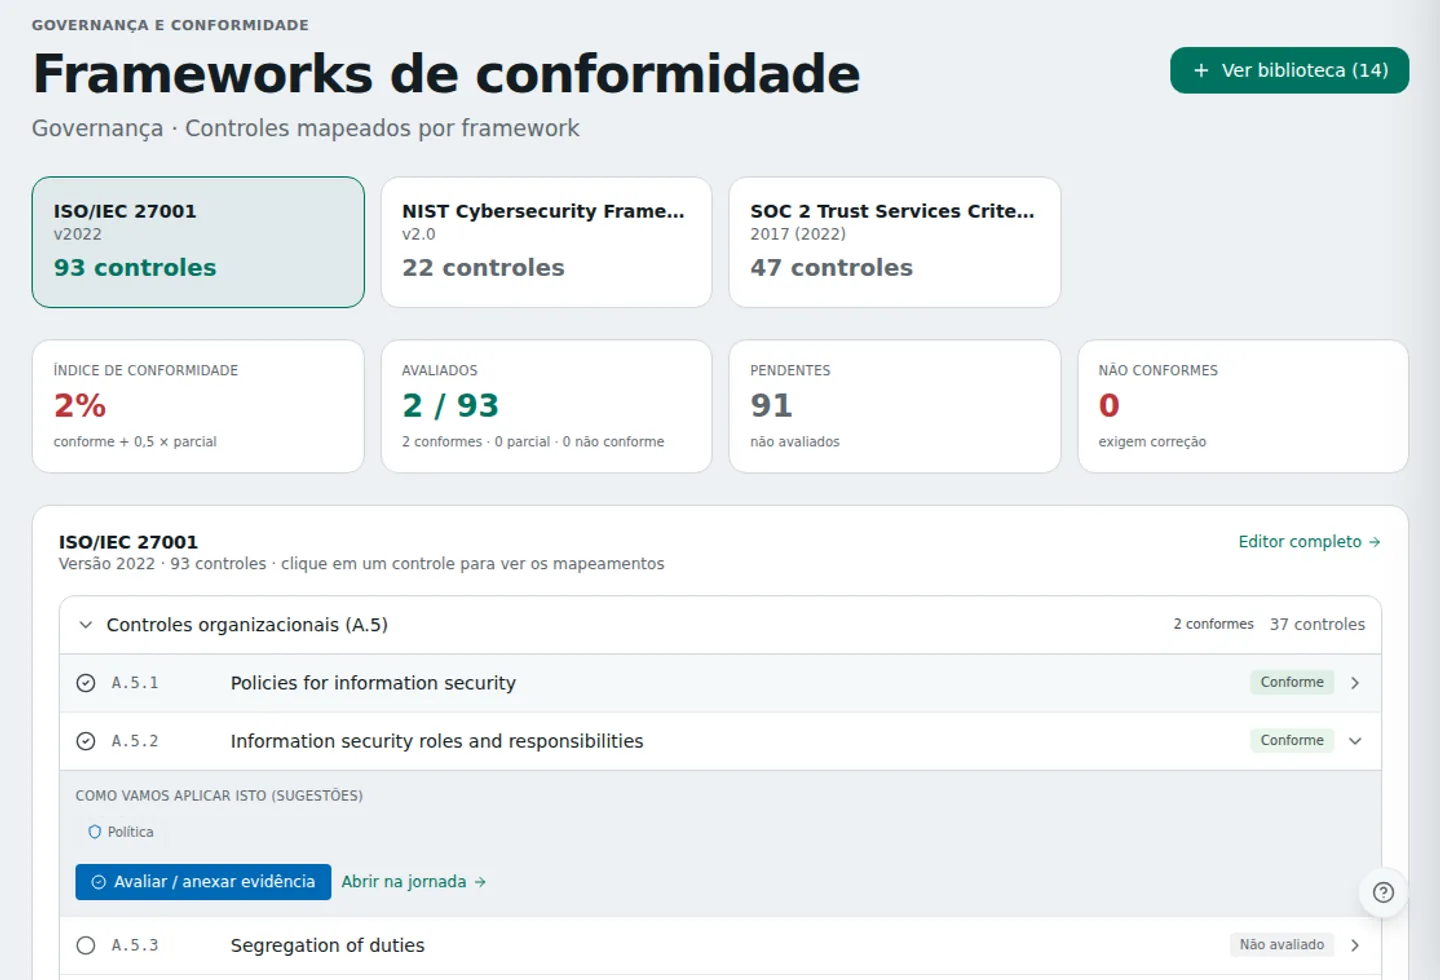
- The standards tracked on the platform: ISO/IEC 27001, NIST CSF and SOC 2.
- The compliance index and how many controls have been assessed.
- Each control with its status and the button to attach evidence.
How to hire us
Every contract starts with a fixed project. It ends with a proposal for an ongoing service, if that makes sense for you.
- Fixed project
- Scope, timeline and price agreed before we start. It takes 2 to 4 weeks and ends with the report and the plan.
- Ongoing service
- An assigned analyst looks after your environment every month, with a monthly report and evidence on the platform.
Frequently asked questions
Does Hegeon issue the ISO 27001 certificate?
Certification is issued by an accredited certification body. Our work is to prepare your company and organize the evidence the auditor will ask for.
When does awareness training start?
The first phishing simulation campaign happens within 30 days of contract signature.
What does a vCISO do?
They take on information security management under contract: set priorities, track risks and present progress to the board.
How many controls does the platform include?
ISO/IEC 27001:2022 comes with the 93 Annex A controls. SOC 2 comes with 47 criteria, and NIST CSF 2.0 is loaded too.
Where is the evidence kept?
On the platform, linked to the control it refers to, with the date it was produced and its validity status.
Do small companies also need to comply with the LGPD?
Yes. The LGPD applies to any company that processes personal data in Brazil, whether from clients or employees. The ANPD published simplified rules for small processing agents, but they do not exempt the company from the law. Compliance starts by knowing what personal data the company holds, where it is stored and who it is shared with.
How long does LGPD compliance take?
The timeline depends on how many systems and processes handle personal data, so it goes into the proposal after the first conversation. The work starts with mapping personal data. That mapping produces the gaps, the compliance plan and the evidence, which is recorded on the platform with the date of each item.
Talk to a specialist for 30 minutes.
Tell us what your company needs. You leave the call with three priorities for your environment.
Prefer to write? Use the email contato@hegeon.com.br.